Skip to content
Platform

One map. One policy. One ledger.

Humans, service accounts, vendors and AI agents. One map, one policy envelope, one ledger.

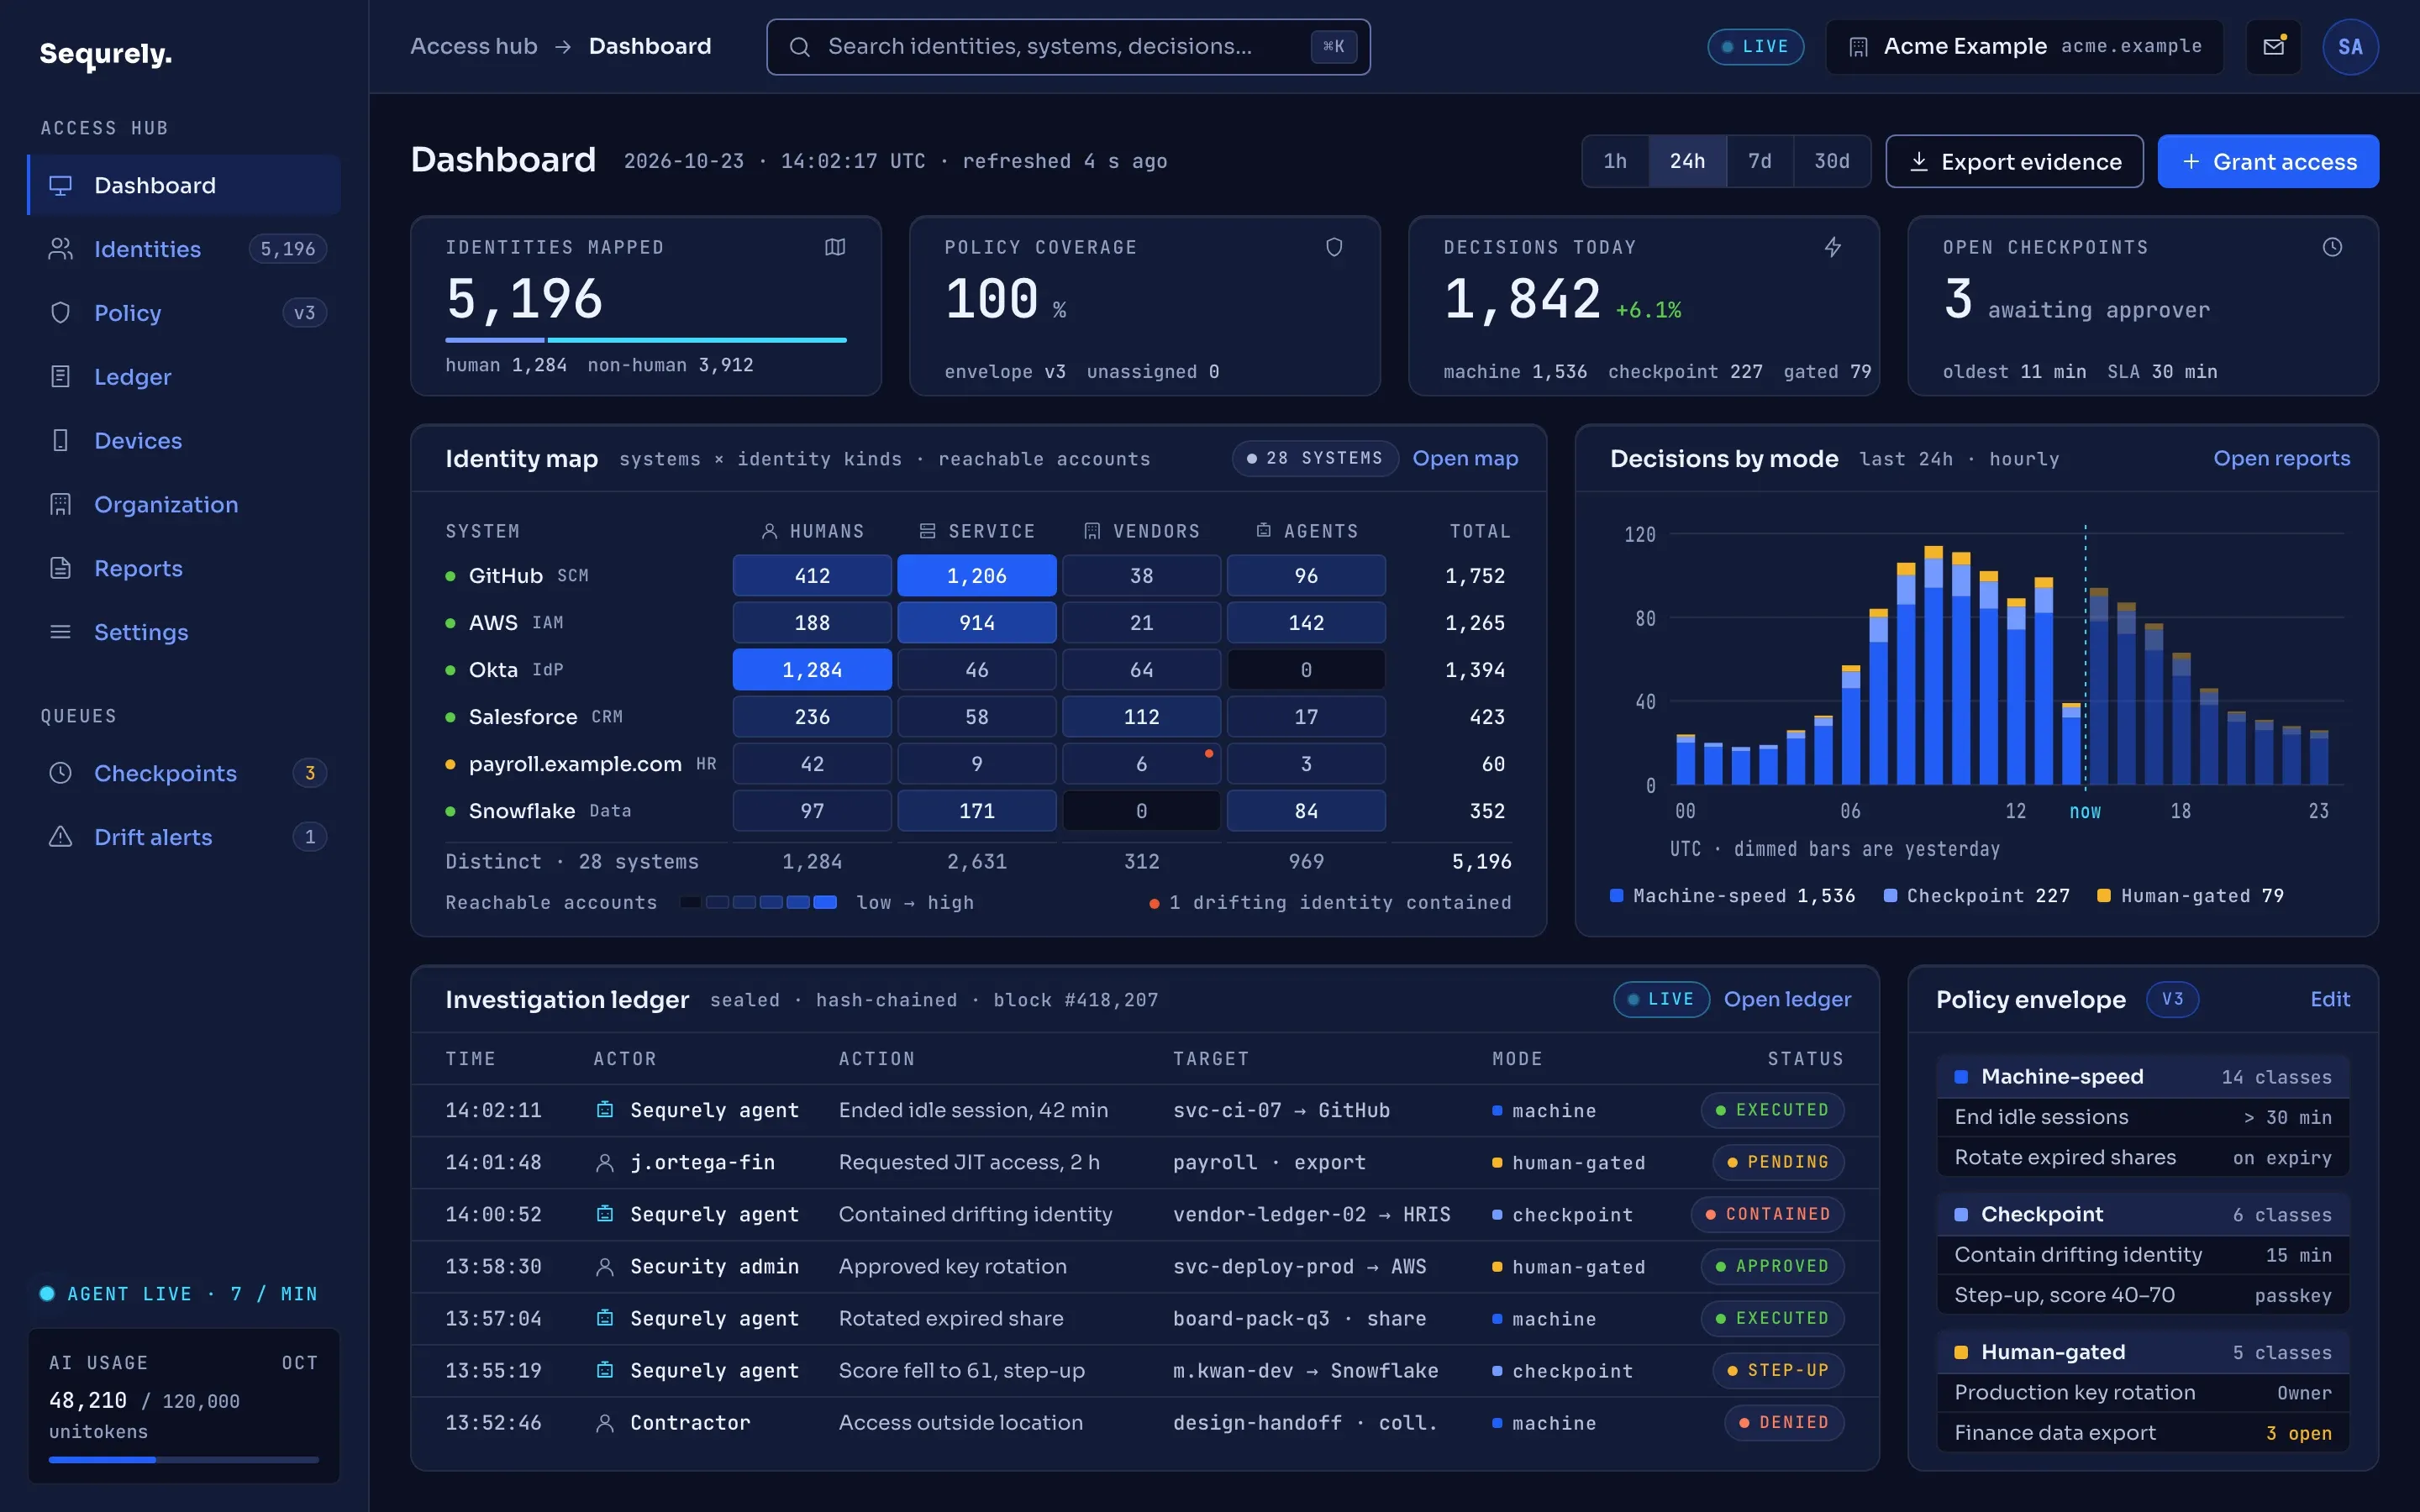
Sequrely admin console dashboard for Acme Example showing 5,196 mapped identities, 100% policy coverage, 1,842 decisions today and 3 open checkpoints, with an identity map of systems by identity kind, a stacked hourly chart of decisions by autonomy mode, a live hash-chained investigation ledger, and the policy envelope v3 action classes.
Sample data. The admin console dashboard: identities mapped, decisions by autonomy mode, the sealed ledger and the policy envelope in one view.
The product

Everything in one product.

One vault, one map and one policy, reached from every surface a person or a system works on.

Browser extension, mobile apps and desktop client

The extension for Chrome and Firefox is the primary access point: it fills, signs in with passkeys and shows what is shared with you. The iOS and Android apps approve, share and hold the vault on the move; the desktop client does the same at a workstation. Credentials are encrypted on the device with AES-256 and per-user, per-device keys before they sync. Nothing arrives at Sequrely’s servers in plaintext.

CHROME · FIREFOX · IOS · ANDROID · DESKTOP

Passkeys and strong sign-in

Passkeys and WebAuthn by default; TOTP and SMS where a target still needs them. Sign-in is bound to authorized devices.

PASSKEYS · TOTP · SMS

Time-limited sharing with an audit trail

Share a credential to a person or a collection for a bounded window. Every share, view and revocation is recorded and expired shares rotate.

SHARES · VIEWS · REVOCATIONS

Organizations, roles, collections and groups

Owner, Admin, Manager and User roles, enforced server-side. Collections and groups scope who sees what, by team and by system.

OWNER · ADMIN · MANAGER · USER

Device inventory and revocation

Each device holds its own keypair. A master device authorizes or revokes the others, and the inventory lists every authorized endpoint with platform, last-active and status.

PER-DEVICE KEYS · MASTER DEVICE

Admin console and audit log

Dashboard, SOC view, agentic reports, organization and policy editors in one web console. Every admin action lands in the sealed ledger.

DASHBOARD · SOC VIEW · REPORTS

Real-time notifications

Share requests, approvals, checkpoints and revocations reach the right person as they happen, on the device they hold.

PUSH · EXTENSION · MOBILE

The Sequrely agent

Ends idle sessions, rotates expired shares, contains drifting identities and grants just-in-time access with a named approver. It never executes a human-gated action.

MACHINE-SPEED · CHECKPOINT · HUMAN-GATED
Extension · Mobile · Desktop

Every surface, one vault.

The extension fills and signs in. The phone approves, shares and carries the vault. The keys stay on the device that made them.

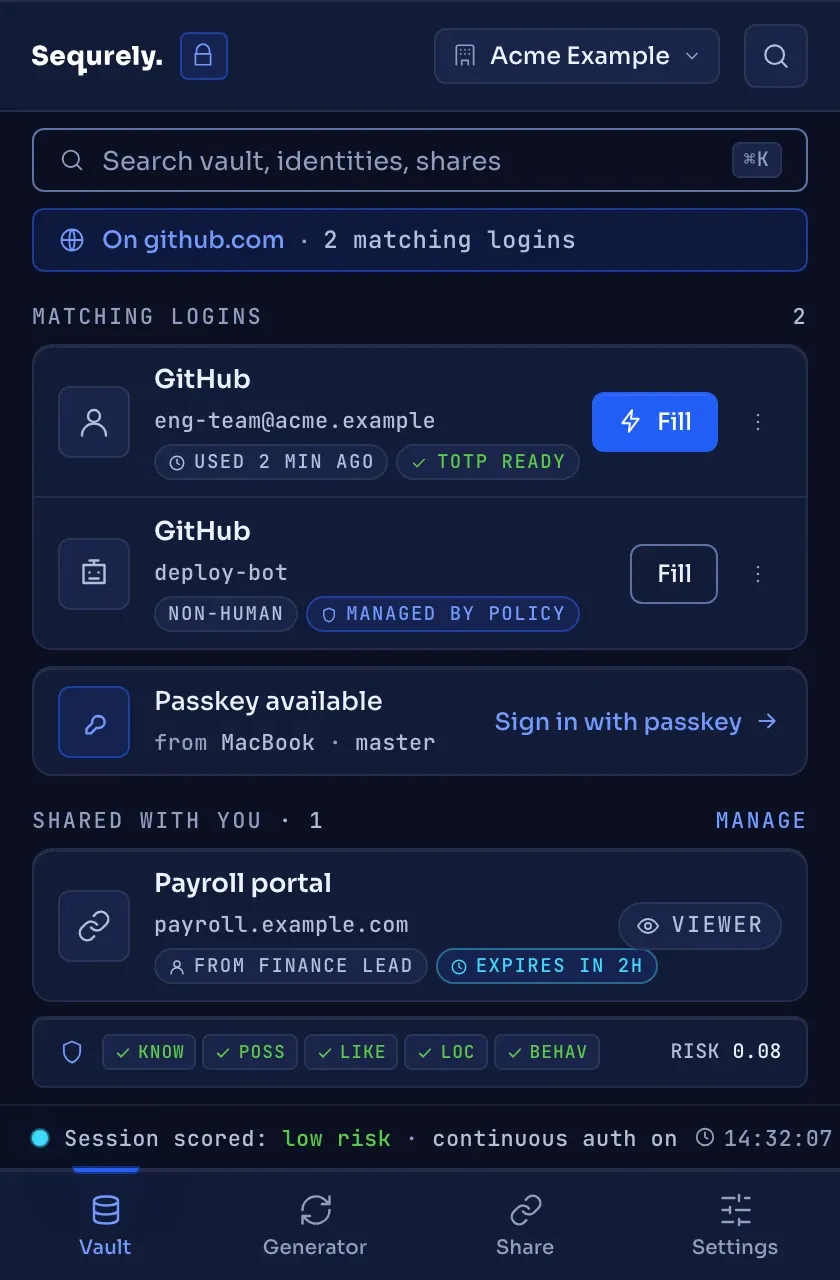
Sequrely browser extension popup on github.com showing two matching logins with Fill buttons, a passkey sign-in row, a time-limited share from the Finance lead with Viewer access and a session scored by five signals.
Sample data. The extension popup on a sign-in page: matching logins, a passkey, a time-limited share and the session score.
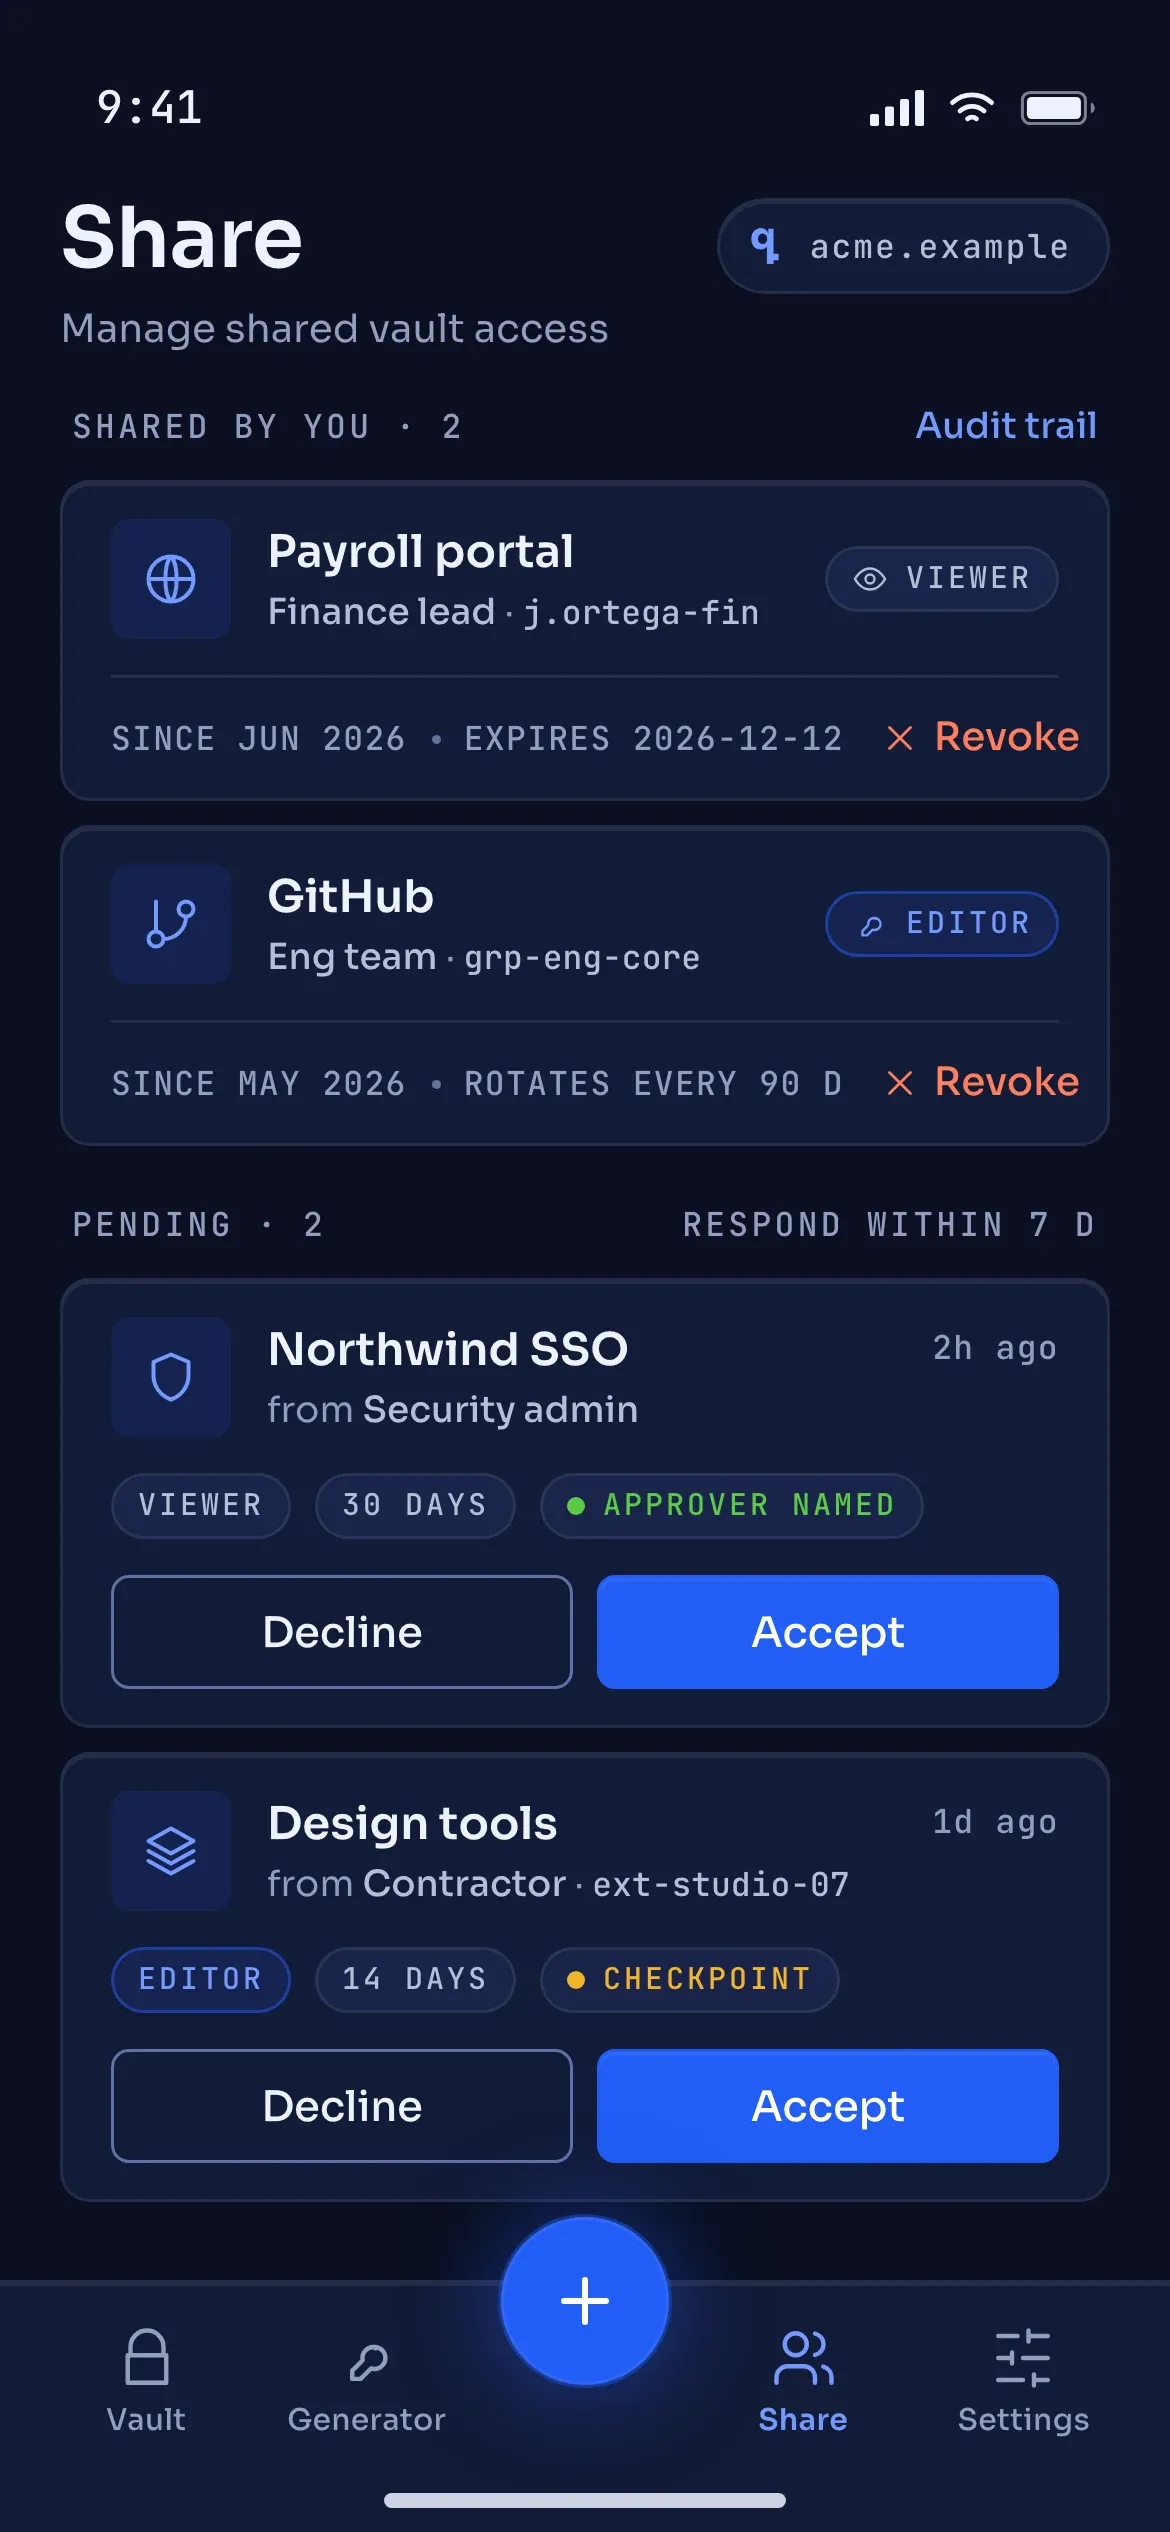
Sequrely mobile app Share screen listing two vault shares you granted (Payroll portal to a Finance lead as Viewer, GitHub to the Eng team as Editor) with expiry and revoke controls, two pending share invitations from a Security admin and a Contractor with Decline and Accept buttons, and a bottom tab bar with Vault, Generator, Share and Settings.
Sample data. Shares you granted, with expiry and revoke controls, and invitations waiting on you.
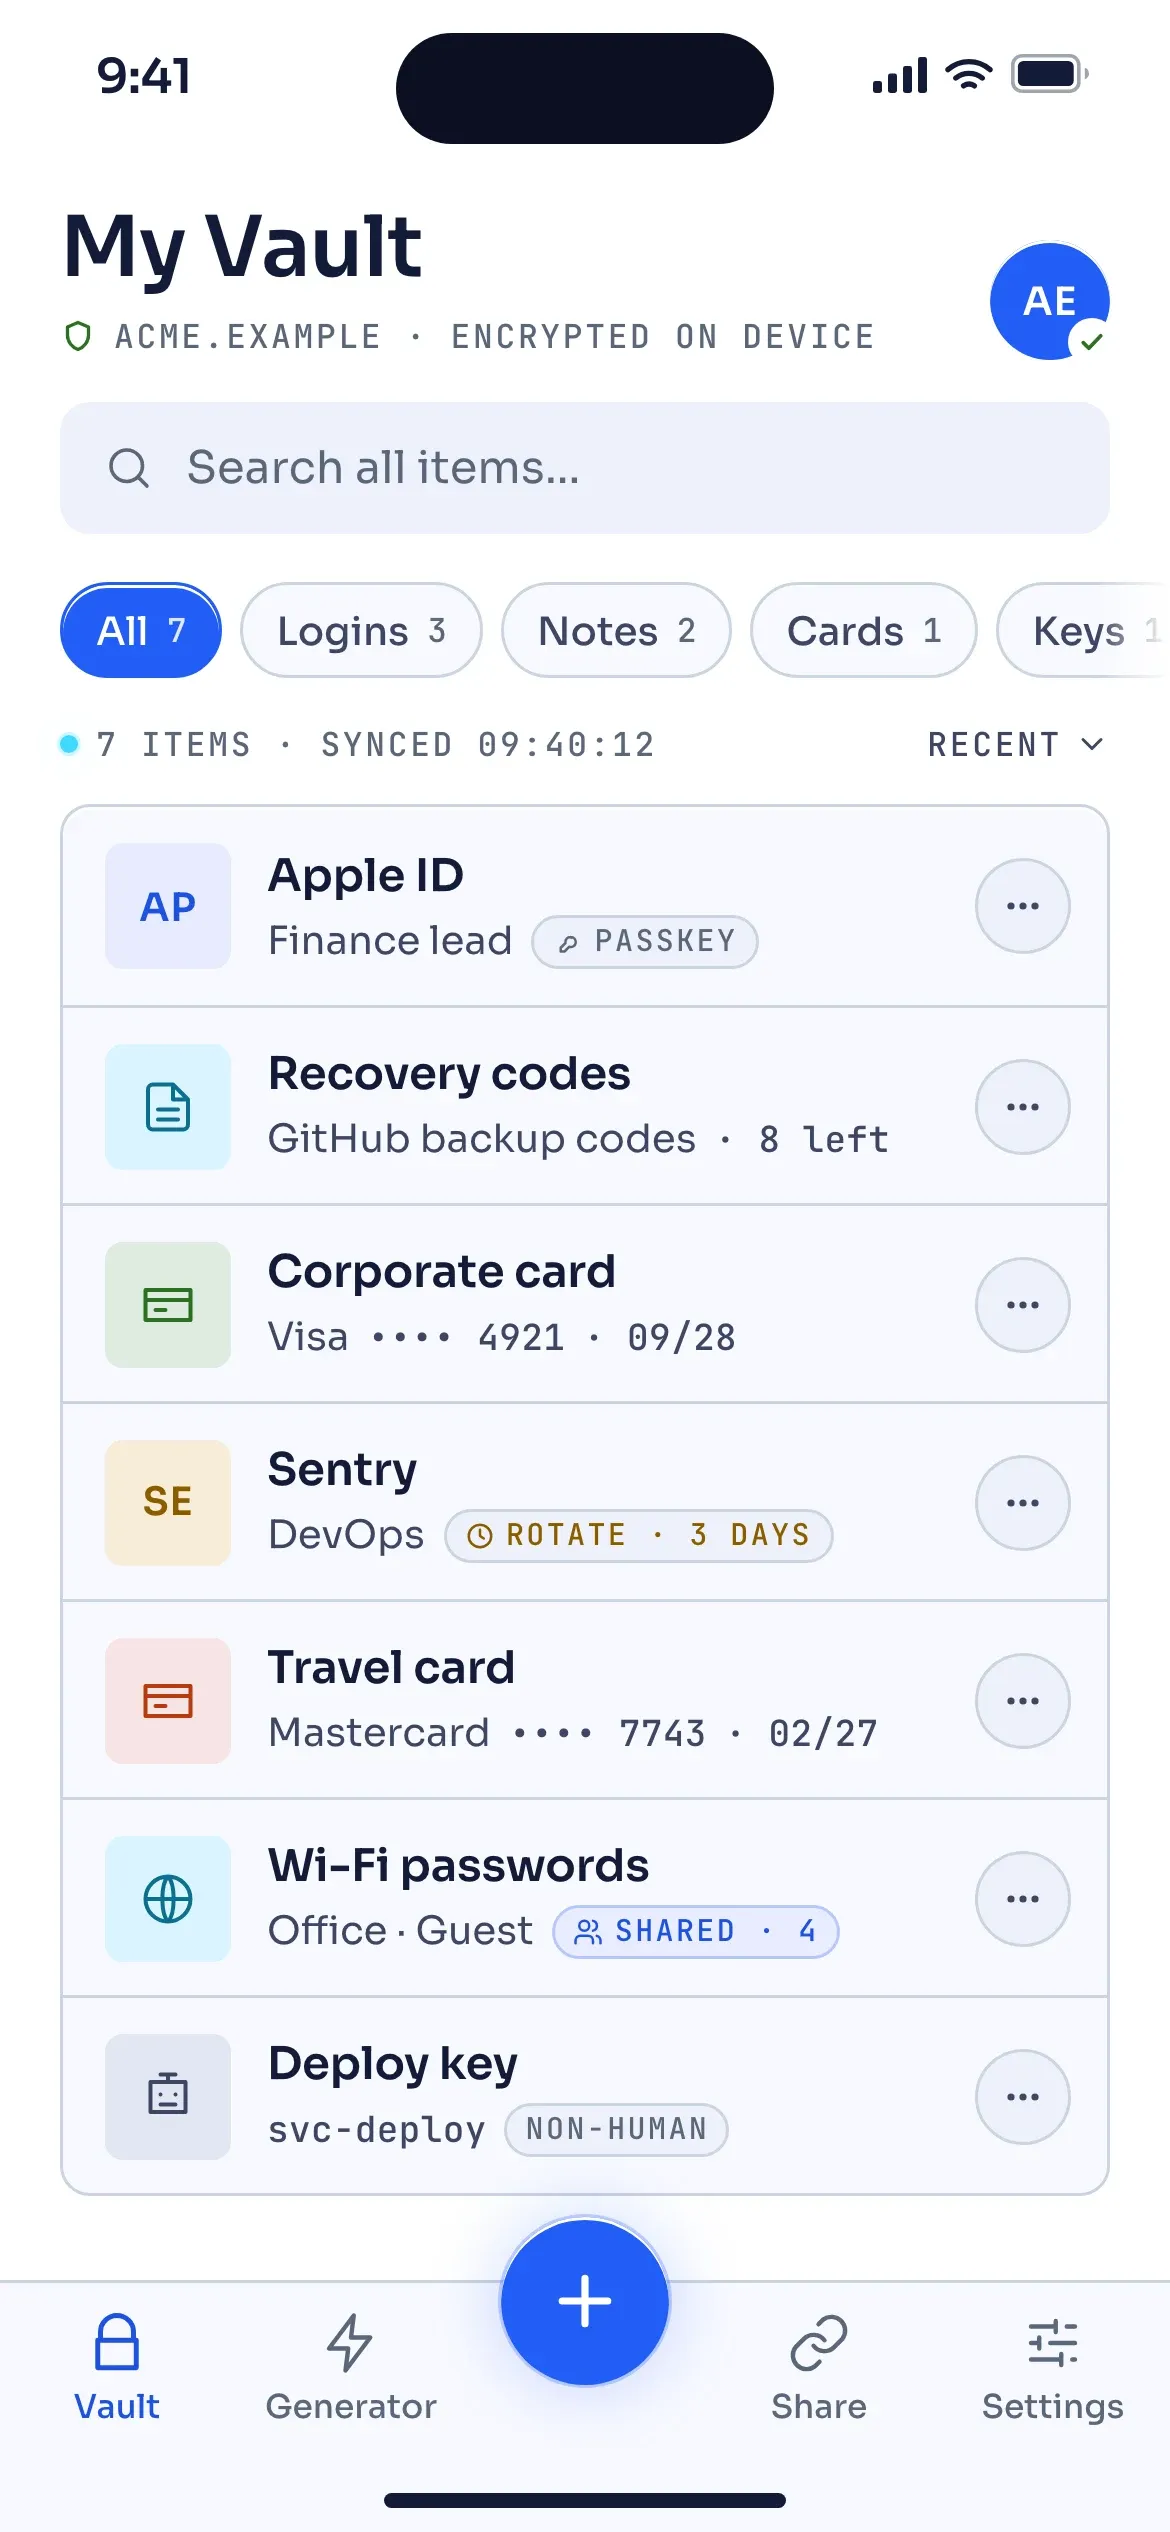
Sequrely iOS app, My Vault screen in light theme: a search field, filter chips for logins, cards, notes and keys, a list of vault items with system names and last-used times, and a bottom tab bar with Vault, Generator, Share and Settings.
Sample data. The vault on a phone: search, filters and every item decrypted only on this device.
Organization

Organizations, roles and devices.

Users, services, roles and devices in one admin view, with every admin action on the record.

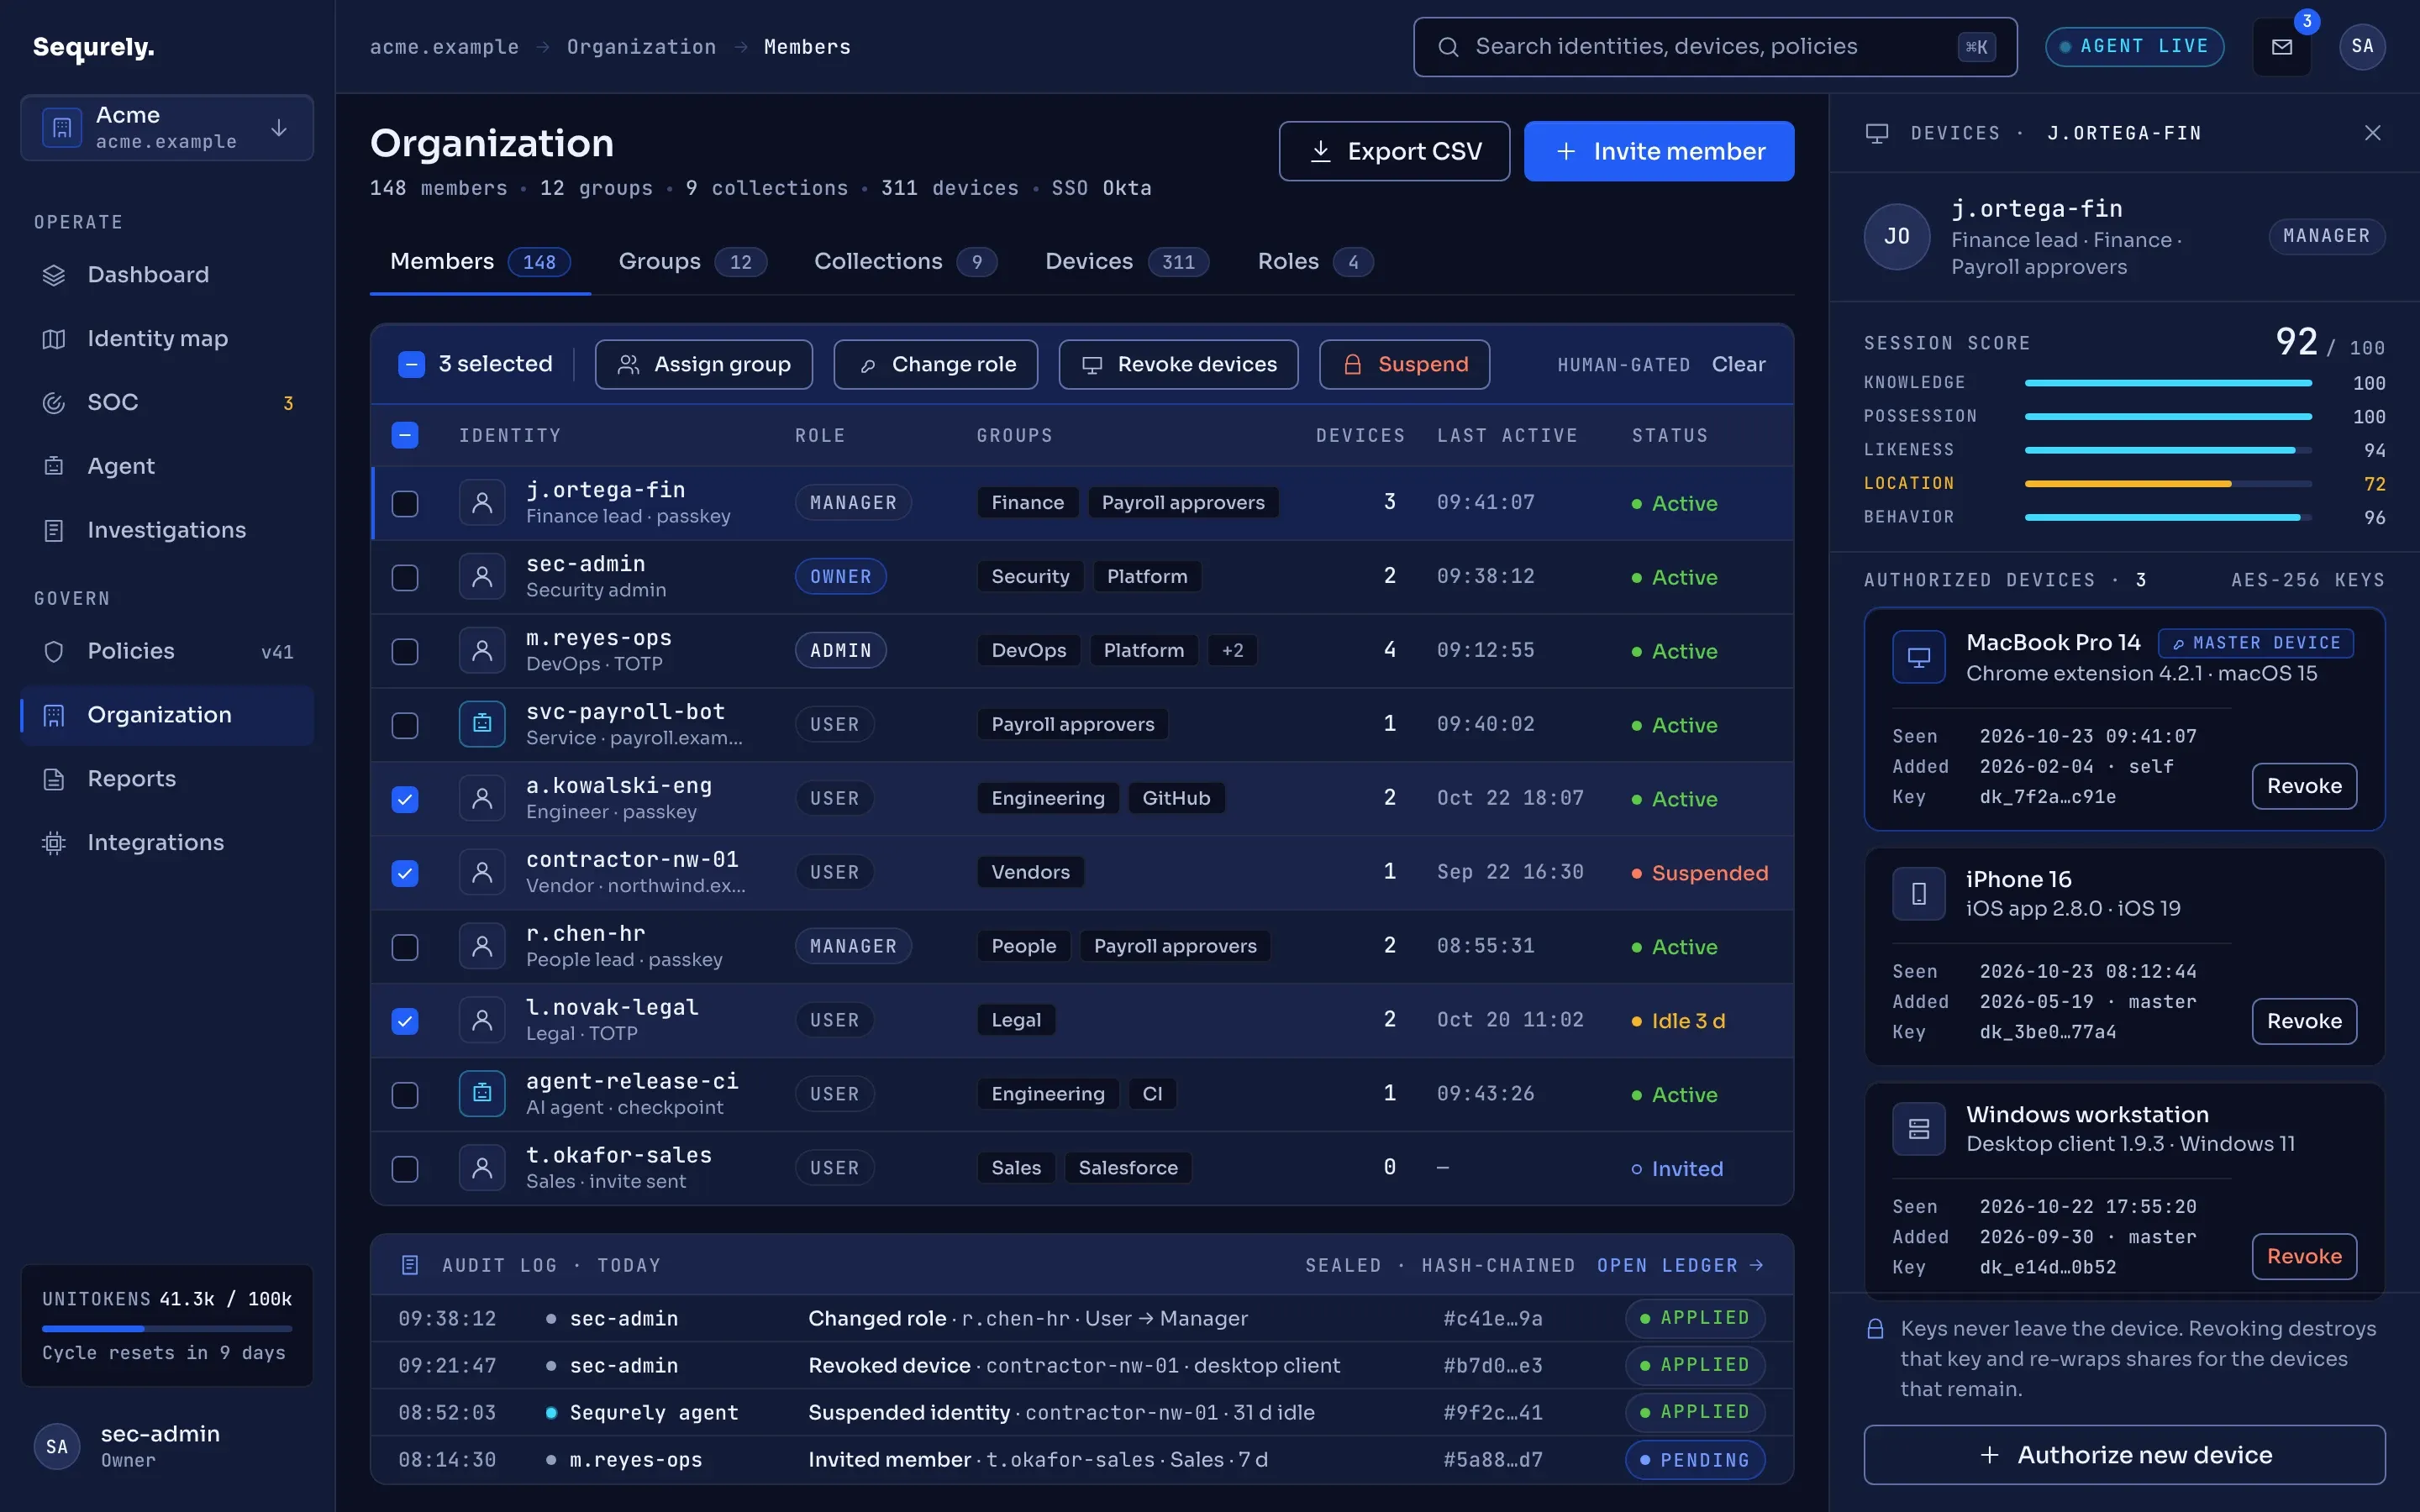
Sequrely admin console on the Organization page: a members table with role chips, groups, device counts and status, a bulk-action bar with three selected, a side panel listing an identity's three authorized devices with a master-device tag and Revoke buttons.
Sample data. The organization page: members with roles, groups and device counts, and one identity’s authorized devices with revocation from the master device.
Roles

Four roles, enforced server-side

Owner, Admin, Manager and User. Collections and groups narrow each role to the systems a team touches.

Devices

Every device, its own keypair

A master device authorizes or revokes the rest. Revocation takes effect at the next sync and is written to the ledger.

Audit log

Every admin action on record

Role changes, invitations, revocations and policy edits are sealed into the same hash-chained ledger as the agent’s decisions.

The enforcement model

Visibility first. Then control.

You cannot enforce what you cannot see. The map comes before the policy, and the policy before the agent.

One map of every identity

Endpoints, cloud, identity logs and non-human accounts collapse into one authoritative map: every identity, human or agent, and the systems it can reach. Fragmentation is where access hides. The map is where it stops.

HUMANS · AGENTS · VENDORS · SERVICE ACCOUNTS

Agentic inventory

Non-human identities are identified explicitly, so service accounts and AI agents are mapped to least privilege instead of inherited access.

NON-HUMAN · LEAST PRIVILEGE

Command and control

Maintain, rotate or revoke the credentials you hold in Sequrely from one place, by hand or by the agent, with each action recorded.

ROTATE · REVOKE · RECORD

Continuous authentication

Knowledge, possession, likeness, location and behavior score the session while it runs. Risk steps up authentication or ends the session.

5 SIGNALS · EVERY SESSION

Access lifecycle

Grants carry an expiry. Vendors and auditors get just-in-time, task-scoped access that revokes itself when the task ends.

TIME-LIMITED · JUST-IN-TIME
Pillar 01 — Continuous authentication

Trust is scored, not granted once.

A login is a point. A session is a line. Five signals keep scoring the line.

01

Knowledge

A PIN or secret only the person holds. Never the only factor.

PASSKEYS · TOTP
02

Possession

An authorized device or hardware key, bound by a keypair that never leaves it.

DEVICE KEYPAIR
03

Likeness

Biometrics through the device’s own secure hardware. Sequrely never sees the template.

DEVICE BIOMETRICS
04

Location

Network, geography and device context. A valid token from the wrong place is still wrong.

NETWORK · GEO
05

Behavior

Drift from the identity’s digital twin: timing, scope, volume. The signal attackers cannot copy.

DIGITAL TWIN
Bounded autonomy

Three modes. One policy.

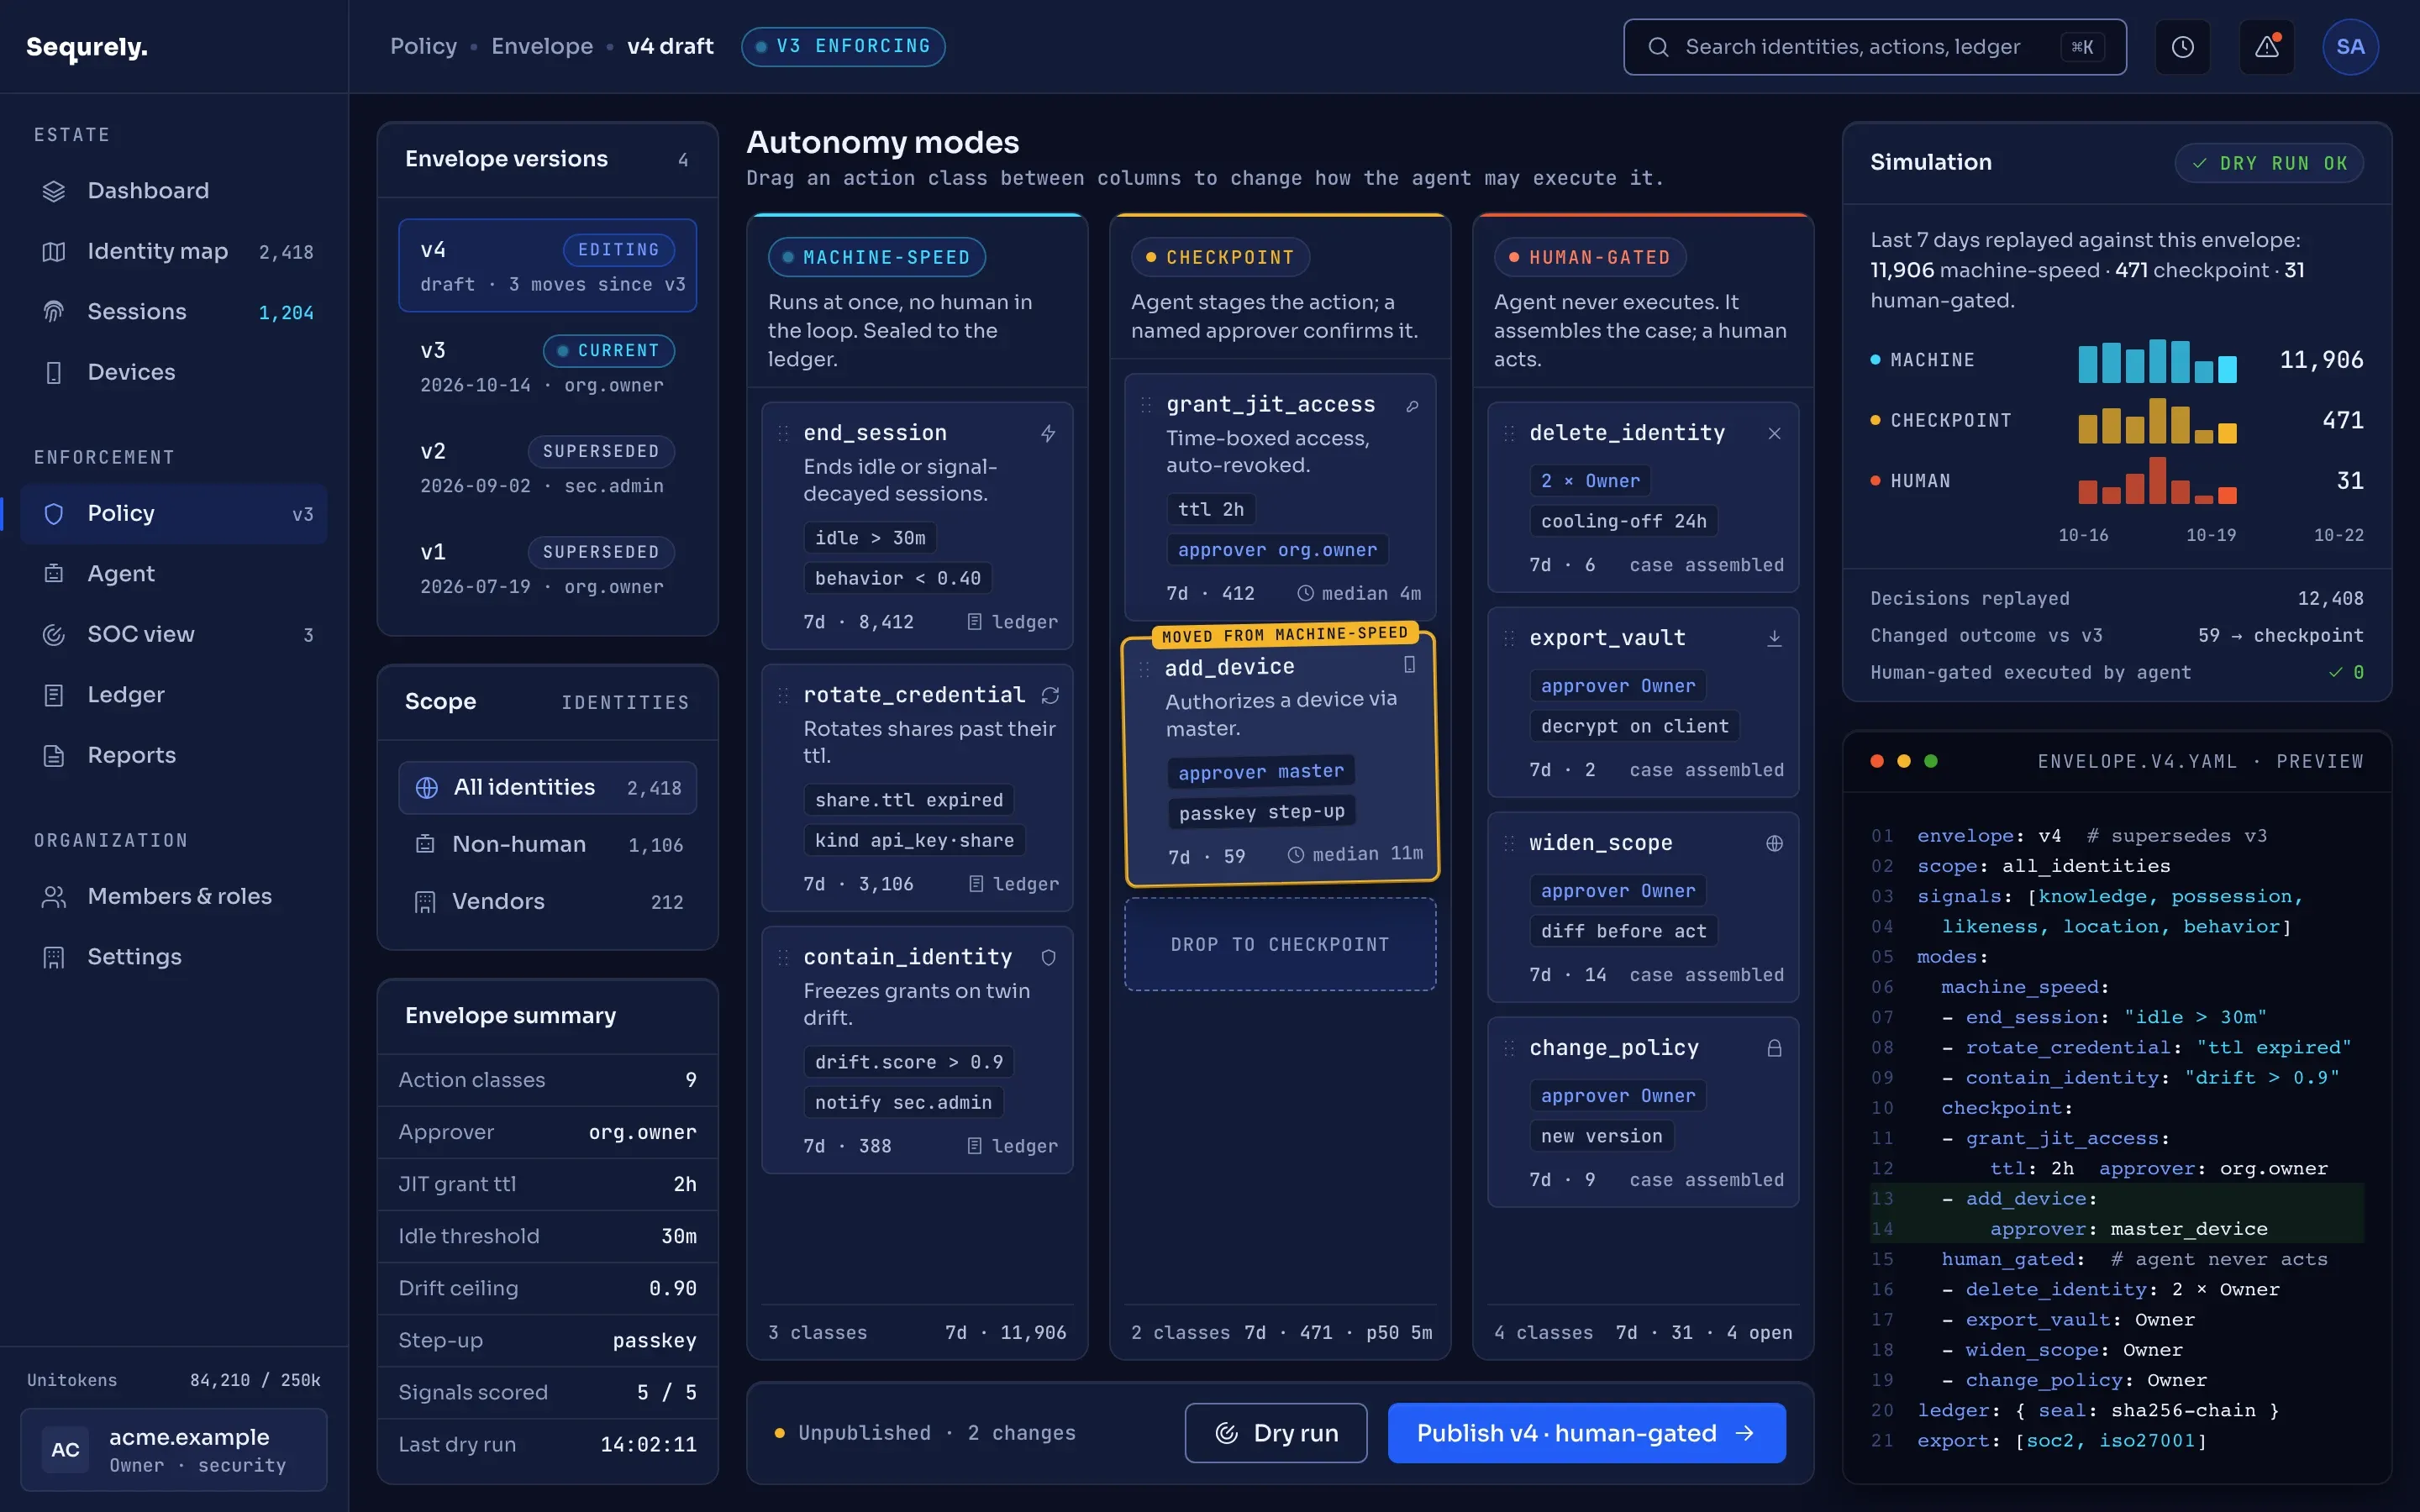
Every action class is assigned a mode in a versioned policy envelope. The agent cannot promote itself.

  • MACHINE-SPEED autonomous within policy
  • CHECKPOINT approve and audit
  • HUMAN-GATED always a person
  1. Observe the baseline

    The digital twin learns each identity’s normal before anything is enforced. Observe mode is the default for a new identity.

  2. Classify the action

    The response is looked up in the policy envelope. The mode comes from the policy, never from the agent.

  3. Act or ask

    Machine-speed runs now. Checkpoint waits for a named approver. Human-gated produces a recommendation and stops.

  4. Seal the record

    Decision, evidence and mode are hashed into the ledger with the hash of the entry before.

  5. Review and tune

    Read the ledger, tighten or loosen the envelope. Changing the envelope is itself a logged, human-gated event.

Sequrely admin console showing the policy envelope editor: a draft v4 envelope with action classes arranged in three autonomy columns (machine-speed, checkpoint, human-gated), a versions and scope panel on the left, and a seven-day simulation with a YAML preview on the right.
Sample data. The policy envelope editor: action classes in three autonomy columns, versions and scope, and a seven-day simulation before the draft is sealed.

Investigation ledger

Sample data: investigation ledger. Example row: 14:02:11, Sequrely agent, New non-human identity found · ci-runner-7 · unmapped, status Watching.

Sample data. Identifiers are fictional. Every row is sealed with the hash of the row before it.

{"ts":"2026-10-23T09:42:14Z",
 "actor":"agent","mode":"machine_speed",
 "action":"end_session","target":"svc-payroll-bot",
 "rule":"idle>30m","seal":"sha256:7f3a…c91e",
 "prev":"sha256:b02d…4e77"}
{"ts":"2026-10-23T09:43:31Z",
 "actor":"human:org.owner","mode":"checkpoint",
 "action":"grant_jit_access","target":"vendor-auditor",
 "ttl":"2h","seal":"sha256:1e8c…a0f3",
 "prev":"sha256:7f3a…c91e"}

Sample data. The JSONL export: one record per decision, each carrying its seal and the hash of the entry before. Exports map to SOC 2 and ISO 27001 controls.

Integrations

Works across the stack you already run.

Enforcement sits beside your identity provider and your cloud IAM; it does not replace them.

SSO / IdPHRISCloud IAMSource controlCRMERPData warehouseTicketingCI runnersAI agents

System categories, not endorsements. The connector list is available on request.

Access under control.
Audits without panic.

Every capability on this page is in the product today.